Today's Encryption Could be Tomorrow's Problem
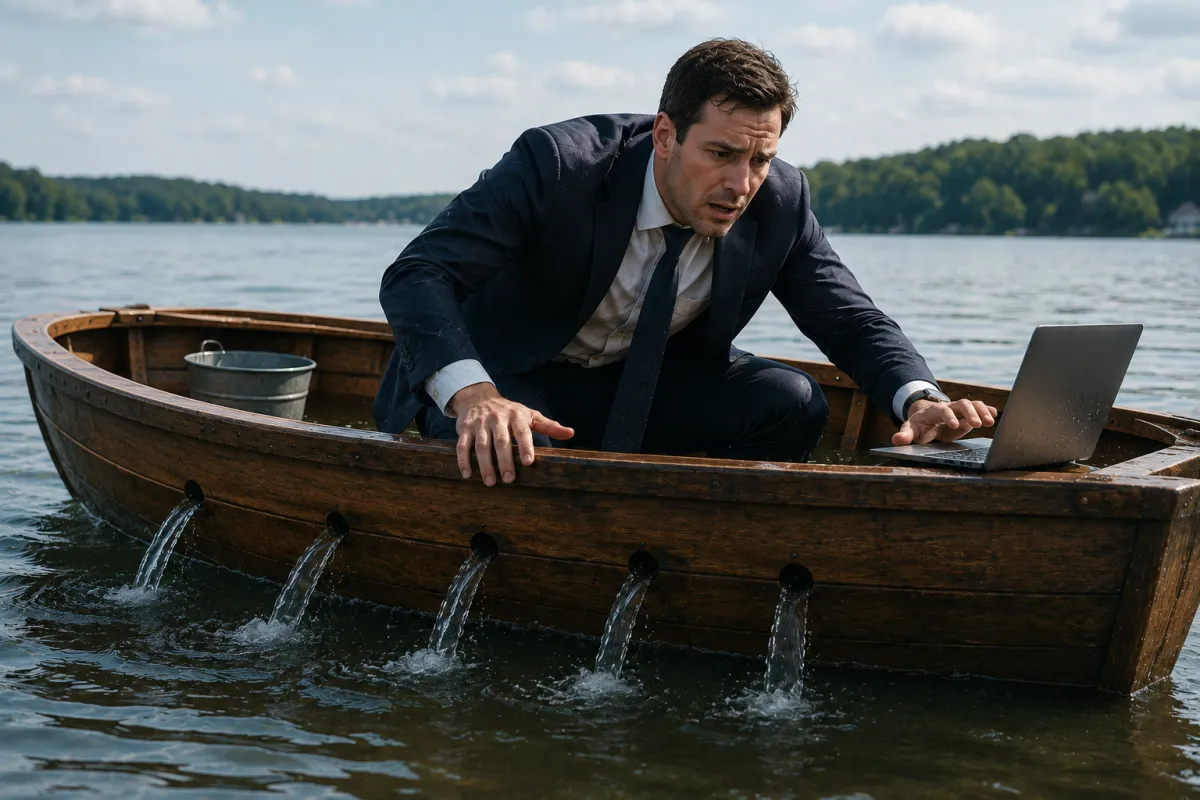
A boat can look like it’s moving along fine while water quietly fills the hull below deck. Your encryption can look the same way.
It’s doing exactly what it’s supposed to do today. It may also be creating a problem your organization is not yet equipped to solve.
The threat is not that quantum computers will make today’s encryption useless overnight. It is that many organizations do not have a complete map of their vulnerable cryptography across applications, infrastructure, devices, certificates, integrations, and vendor-managed systems. That gap remains hidden long before anything visibly breaks, and an organization can look secure while a migration problem accumulates beneath the surface.
The Hard Part Starts Before the Migration
Post-quantum cryptography is often discussed as a future transition: when the threat becomes real, organizations swap vulnerable encryption for quantum-resistant alternatives.
That framing skips the actual work.
You cannot replace what you cannot find.
Cryptography sits in more places than most leaders ever see — in applications, authentication systems, network infrastructure, embedded devices, software libraries, certificates, cloud services, vendor platforms, and the integrations connecting it all.
Someone has to find those dependencies before anything changes, then determine what each one supports, who owns it, whether it can be upgraded, what else depends on it, and whether a vendor controls the change.
That inventory work — unglamorous, cross-functional, easy to defer — is where the real risk lives.
It’s an operational problem wearing a technical disguise.
Uncertainty Has a Business Cost
An organization that cannot locate its cryptography cannot estimate what changing it will cost, how long the work will take, which systems will be hardest to touch, which vendors must participate, or what could break during testing.
It also cannot prioritize effectively — deciding which sensitive data needs protecting first because it has to stay confidential for years.
Without that visibility, an organization can mistake “we haven’t found a problem” for “we have time.”
Those are not the same thing.
And the gap between them grows as the environment expands.
Every new application, integration, device, cloud service, or vendor relationship can add another dependency that eventually needs to be examined.
For data that must remain sensitive for years, the exposure compounds differently: information captured today can remain valuable long enough for future decryption to matter.
Knowing exactly what you are protecting, where it sits, and how long it must remain confidential turns that risk into something leaders can actually manage.
The Questions Leaders Should Be Asking
“Are we ready for post-quantum cryptography?” is too broad to answer.
Take it to your team instead as a short, specific set:
Do we know where our cryptography sits, who owns it, and how difficult it would be to change?
Which critical systems run on vulnerable public-key cryptography?
Which of those systems will resist upgrading?
Which dependencies sit with third parties, not us?
Do those vendors have credible migration plans — not just general assurances?
These questions immediately expose whether the organization has enough visibility to build a credible plan.
Ownership is the fault line here.
Cybersecurity can coordinate the effort, but application owners, infrastructure teams, architects, procurement, operations, and risk leaders each control a piece of the answer.
When nobody can name the owner of a given dependency, that gap is the risk.
Start With One Critical Area
Skip the enterprise-wide transformation.
Pick one critical application, business service, sensitive data flow, or operational environment.
Map its cryptography. Separate what is internally controlled from what depends on vendors. Name the owners. Estimate what actually has to change.
The goal is not a technology purchase.
It is finding out whether the organization understands its own cryptographic environment well enough to plan with confidence.
The biggest post-quantum risk is not that today’s encryption eventually goes obsolete.
It is discovering, too late, that no one ever knew where all of it was.
A focused 15-minute review can show you where your scattered encryption risk runs deepest — and what to investigate first. Click here to schedule a call.