When Hackers Turn Your Equipment Against You
A cyberattack can destroy your inventory without stealing a single piece of data.
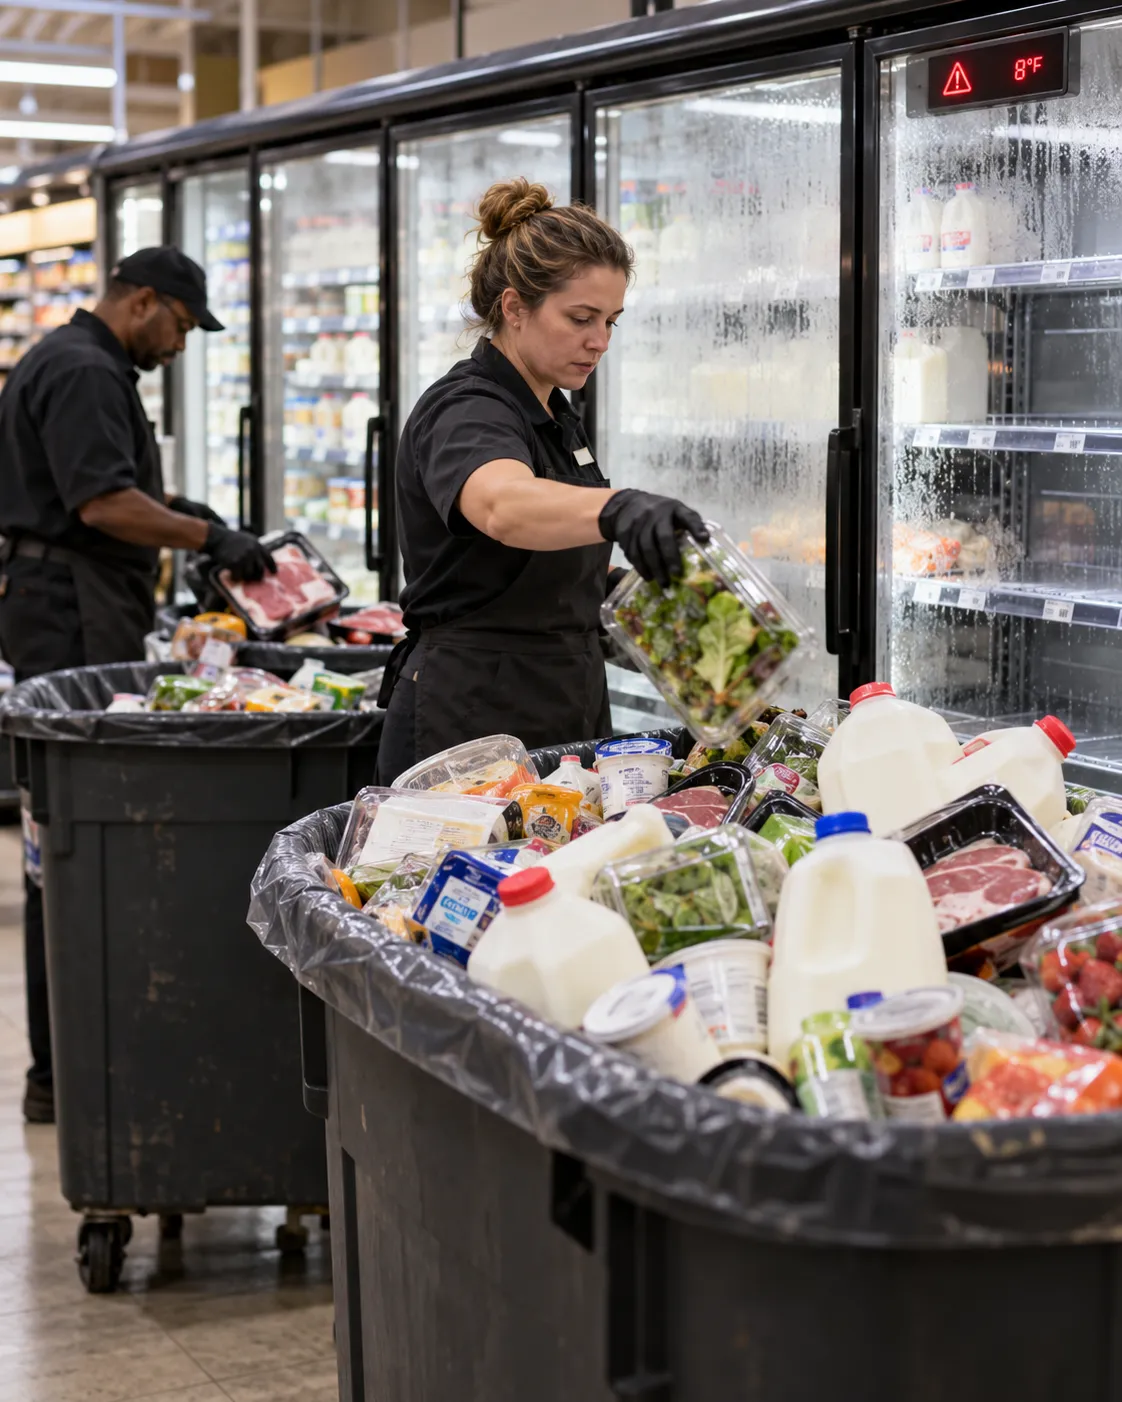
In France, supermarket employees filled overflowing trash cans with milk, meat, produce, and other perishables after hackers manipulated refrigeration controls.
The equipment wasn’t simply malfunctioning. Hackers were manipulating the controls that governed its operation.
Several hundred stores were affected. Intermarché reported that fridges at about 150 of its stores ran as hot as 122°F (50°C) for six hours (Reuters), and prosecutors cited both food losses and fires (Associated Press).
The question that matters isn’t whether your organization operates refrigerators. It’s whether someone could remotely manipulate the equipment your business depends on, and what that would cost you.
The exposure sits beyond your data and networks
Businesses rely on operational technology (OT) to control physical processes: manufacturing equipment, refrigeration, environmental controls, and building automation.
Many of these systems accept remote connections, so technicians can adjust settings, diagnose problems, and perform maintenance without visiting the site.
That’s convenient, until access falls into the wrong hands.
In France, hackers reportedly exploited older refrigeration control software, changing temperature settings and extending defrost cycles. Some changes delayed alarms, giving the damage more time to develop (Le Monde).
The attackers used functions already built into the equipment. Traditional cybersecurity programs concentrate on data, applications, and business networks, so equipment controls may receive less attention, especially when installed years ago or maintained by outside vendors.
Who owns the risk when systems cross departmental lines?
Consider a manufacturer whose production equipment a third-party specialist maintains.
Operations runs production. Facilities coordinates maintenance. IT protects the network. The vendor handles software updates and remote troubleshooting.
Who decides whether that vendor still needs remote access? Who reviews the security settings? Who confirms that known vulnerabilities have been fixed?
Researchers disclosed security flaws in Danfoss refrigeration controllers in August, and the manufacturer released firmware to address them. Danfoss confirmed that affected systems were running outdated firmware, although investigators have not established whether the disclosed vulnerabilities were exploited in these attacks.
Without assigned responsibility, each department may assume another has it covered. The result is an expensive accountability gap, even when every department does its job.
What modern OT security tools reveal
These tools can discover connected equipment, map network communications, identify known vulnerabilities, and flag suspicious activity. Some use passive monitoring, observing traffic without probing sensitive industrial equipment.
Visibility isn’t a fix, though. Not every vulnerability can be corrected with an update. Older equipment may require vendor involvement, scheduled downtime, or replacement. Sometimes restricting remote access or isolating equipment is the faster, more practical response.
Visibility helps determine where to spend limited security resources first.
What should I do about this risk?
Choose one operation where unexpected equipment behavior could interrupt revenue, damage inventory, or endanger employees. Then answer three questions:
Access: Which devices allow remote connections, including vendor access, and are those connections still necessary?
Ownership: Who is accountable for reviewing security settings, updates, and known vulnerabilities?
Business impact: What would six hours of disrupted operations cost, and how quickly could you restore normal operations?
Use the answers to decide whether a detailed OT cybersecurity assessment is justified.
The critical decision isn’t how much to spend on cybersecurity. It’s whether your security priorities reflect what your business can least afford to lose.
Not sure your cybersecurity strategy covers connected operational equipment? A complimentary 15-minute conversation can help clarify where to investigate first.